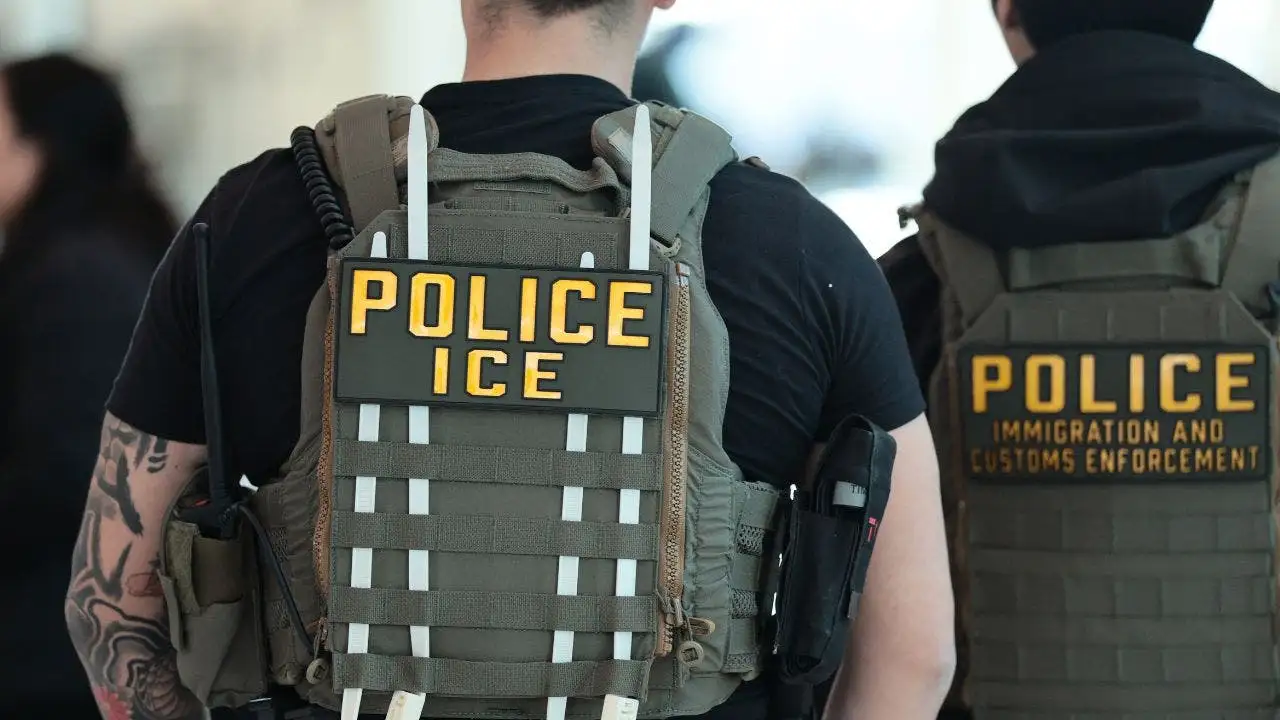

A significant data breach at the Department of Homeland Security (DHS) has exposed sensitive information related to more than 41,000 employees and contractors, raising serious security concerns among federal officials. The leak, which was first reported on October 28 when the nonprofit group Distributed Denial of Secrets published the records, revealed employee names, contact information, and details about undercover and surveillance operations. As the fallout unfolds, both current and former employees are worried about the implications for their safety and the security of ongoing investigations.
| Article Subheadings |
|---|
| 1) Overview of the Data Breach |
| 2) Significance of the Exposed Records |
| 3) Potential Risks to Undercover Operations |
| 4) The Role of Technology in Security |
| 5) Measures for Prevention and Protection |
Overview of the Data Breach
The ongoing investigation into the DHS data breach began on October 28, when the nonprofit organization Distributed Denial of Secrets released a vast trove of records acquired by an unidentified group claiming to have accessed government systems. The release included information pertaining to various DHS personnel across multiple agencies, notably the Immigration and Customs Enforcement (ICE) and U.S. Customs and Border Protection (CBP). The leak caused significant alarm among federal employees, particularly because it revealed not just names and contact information but also organizational structures, office locations, phone numbers, and affiliations with internal projects and groups. The overall scope of this breach underscores the vulnerabilities that exist within governmental cybersecurity protocols and processes.
Significance of the Exposed Records
The breadth of the leaked records is striking, with CBP accounting for over half of the total disclosures. Approximately 10,000 records pertain specifically to ICE, and another 6,200 are linked to U.S. Citizenship and Immigration Services. Despite the volume of exposed information, it remains uncertain whether private home addresses were included in the leak. The last update to these records was on August 19, indicating that some data may already be outdated. However, the public availability of such organizational details presents a unique set of challenges, especially when viewed in conjunction with ongoing national security operations.
Potential Risks to Undercover Operations
One of the most damaging aspects of the data leak involves its implications for undercover operations related to Homeland Security Investigations. Reports have identified numerous employees tied to internal access groups that indicate participation in certified undercover activities. The exposure of personnel involved in such operations raises concerns about ongoing investigations, as the very nature of these assignments relies heavily on confidentiality. Experts have voiced strong apprehension regarding the potential repercussions for agents whose operational details may now be compromised.
“This is a nightmare scenario,”
stated a former acting director of ICE, highlighting the grave risks posed to agents’ safety due to the unintended exposure of their identities.
The Role of Technology in Security
Further complicating the situation are references in the leaked documents to technology platforms that DHS employees might use during investigations. Notable mentions include Palantir’s Falcon platform, known for its analytical capabilities, as well as software designed for surveillance purposes. The leak also revealed connections to artificial intelligence technologies such as OpenAI’s ChatGPT and Google’s Gemini, raising questions about the security of classified and sensitive investigations. While the mere mention of these technologies does not confirm active usage or any wrongdoing, it does expose vulnerabilities in how the department manages information and internal processes.
Measures for Prevention and Protection
Following the breach, the DHS has been working tirelessly to curtail the spread of sensitive information. It reached out to various platforms, including content hosters, in attempts to have the leaked records removed. However, the hosting provider cited workplace contact information rather than private inconsistencies as the reason for declining to comply with the DHS’s request. This episode underscores the difficulties in retrieving potentially hazardous information once it has been publicly circulated. Moreover, security experts have begun sharing strategies for individuals and organizations to protect themselves in a world where cyber breaches are increasingly commonplace.
Some best practices suggested include verifying unexpected calls and emails, strengthening passwords and account security, using robust antivirus software, employing data removal services, monitoring for identity theft, and reporting suspicious activities promptly. By not only understanding the nature of these attacks but also taking proactive steps, individuals can help mitigate their exposure to potential threats emanating from sensitive information leaks.
| No. | Key Points |
|---|---|
| 1 | A data breach at DHS has revealed sensitive details about over 41,000 employees and contractors. |
| 2 | The leaked records raise security concerns, particularly for agents involved in undercover operations. |
| 3 | The exposure of technology used in investigations raises data protection vulnerabilities. |
| 4 | DHS is actively attempting to remove the leaked records from the internet. |
| 5 | Individuals are encouraged to take proactive security measures to protect themselves against potential phishing attacks. |
Summary
The DHS data breach serves as a critical reminder of the vulnerabilities present in governmental cybersecurity practices and the alarming implications for national security. The exposure of sensitive personnel information and operational details can endanger not only agents’ lives but also ongoing investigations. As the department grapples with the aftermath, the onus lies on both officials and individuals to reinforce security protocols and protect data integrity moving forward. The risk of targeted attacks based on leaked information underscores the necessity for heightened awareness and preparedness in an increasingly complex cyber landscape.
Frequently Asked Questions
Question: What is the scale of the DHS data breach?
The DHS data breach has exposed sensitive information concerning over 41,000 employees and contractors, including personal contact details and organizational affiliations within various DHS agencies.
Question: What risks does this breach pose to undercover agents?
The leak poses significant risks to undercover agents as it reveals connections and identities that could jeopardize ongoing operations and put the personnel involved in danger.
Question: What actions is DHS taking in response to the breach?
DHS is actively investigating the breach and has reached out to internet hosting platforms to remove the leaked records, while also prioritizing the protection of its employees and ongoing operations.
