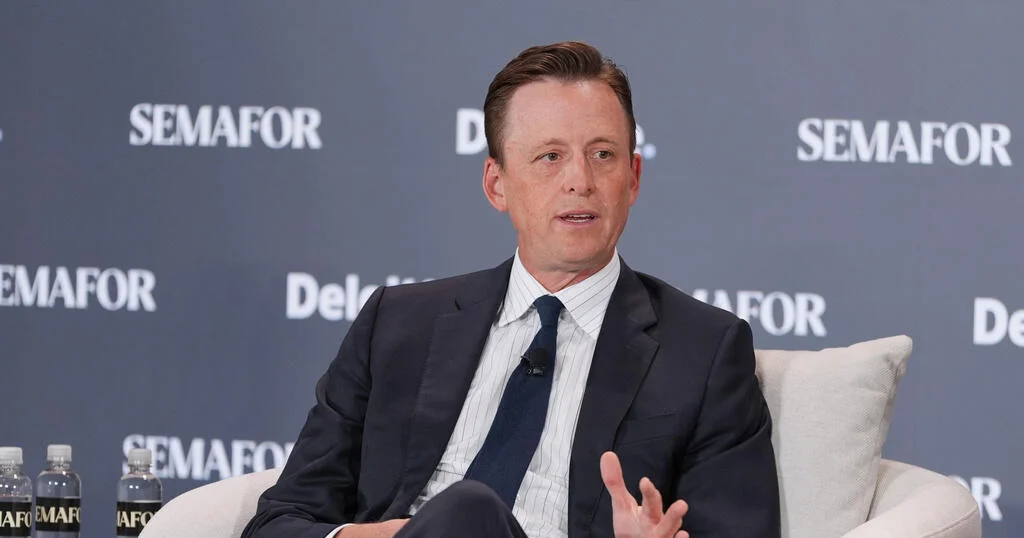

The White House has announced the departure of National Cyber Director Sean Cairncross, who has been in the role since August 2025. Multiple sources indicate that his exit is due to pressure from White House Chief of Staff Stephen Miller, who has questioned Cairncross’s qualifications for the position. As the nation grapples with a series of technological outages affecting various sectors, the White House has appointed Kirsten Davies, the Pentagon’s Chief Information Officer, as Cairncross’s successor, pending Senate confirmation.
| Article Subheadings |
|---|
| 1) Reasons Behind Cairncross’s Departure |
| 2) Profile of the New Cyber Director |
| 3) Recent Technological Outages |
| 4) The National Cyber Director Role |
| 5) Future Implications for U.S. Cybersecurity |
Reasons Behind Cairncross’s Departure
The resignation of Sean Cairncross from his position as National Cyber Director can be traced back to internal evaluations within the White House. Chief of Staff Stephen Miller has reportedly expressed doubts about Cairncross’s expertise in cybersecurity, noting a perceived gap in the necessary skills for this pivotal role. These concerns have been reflected in the decision to initiate a search for a new director almost immediately after assuming his position. The implications of administrative changes such as this one can often signal greater strategic shifts concerning how cybersecurity is managed at the federal level.
Profile of the New Cyber Director
In the wake of Cairncross’s departure, Kirsten Davies, currently serving as the Pentagon’s Chief Information Officer, has been poised to take over as the new White House Cyber Director. This appointment speaks to the administration’s emphasis on selecting a leader with substantial experience in the field of cyber information management. Davies’s qualifications will need to be vetted and confirmed by the Senate before she can assume the role permanently. Her experience at the Pentagon may suggest a strategic shift towards more comprehensive cybersecurity measures within the Department of Defense and across federal agencies, particularly given contemporary threats.
Recent Technological Outages
The timing of Cairncross’s exit coincides with major technological outages that have impacted various essential services across the United States. Reports indicate that these outages have affected Microsoft services, air traffic control systems, banking services, and even the National Security Agency’s (NSA) internal network. According to Markwayne Mullin, Secretary of Homeland Security, investigations have not yet found any evidence linking these outages to foreign adversaries. He expressed confidence that the outages were not indicative of malicious activity from overseas, a reassuring statement amidst ongoing concerns about cybersecurity threats.
The National Cyber Director Role
The role of National Cyber Director was established to serve as the primary advisor to the President on all matters concerning cybersecurity, effectively coordinating strategies across various federal sectors. Since its inception in 2021, the office has overseen multiple initiatives aimed at fortifying the nation’s digital infrastructure against evolving cyber threats. Cairncross himself has been an advocate for making significant changes in how cybersecurity is approached, focusing on proactive deterrents against sovereign adversaries. As the U.S. faces increasing threats from countries such as Iran, Russia, and China, the administration’s strategy for cybersecurity will largely depend on how effectively the new National Cyber Director can orchestrate responses and collaborations across federal agencies.
Future Implications for U.S. Cybersecurity
With strong emphasis placed on technological resilience and strategic response to cyber incidents, Cairncross’s departure and the appointment of Davies signal both continuity and potential change in U.S. cybersecurity strategy. The administration’s cyber strategy, released earlier this year, included ambitious goals focusing on defeating cyber adversaries before they breach critical networks. As U.S. cybersecurity measures come under scrutiny, the successful integration of new leadership will be critical. As stated by Cairncross in previous remarks, the U.S. must establish “costs and consequences” for cyber threats; it remains to be seen how effectively the new appointee can enact this vision.
| No. | Key Points |
|---|---|
| 1 | Sean Cairncross has been removed from his position as National Cyber Director amid concerns over his qualifications. |
| 2 | Kirsten Davies is set to replace Cairncross, pending Senate confirmation. |
| 3 | Recent technological outages affecting key services have raised alarms about national cybersecurity. |
| 4 | The role of National Cyber Director is crucial for coordinating cybersecurity strategy within the federal government. |
| 5 | The new leadership will face the challenge of continuing to adapt the U.S. cybersecurity strategy to evolving threats. |
Summary
The recent changes in leadership at the National Cyber Directorate underscore the challenges facing U.S. cybersecurity efforts amidst increasing technological vulnerabilities. With Kirsten Davies expected to step into the role, the administration is likely poised to reassess and enhance its strategy in the face of escalating cyber threats. The move emphasizes the importance of adaptive leadership in the pursuit of safeguarding national interests amid a rapidly evolving digital landscape.
Frequently Asked Questions
Question: What led to Sean Cairncross’s removal as National Cyber Director?
Sean Cairncross was removed due to concerns from White House officials, particularly Chief of Staff Stephen Miller, over his qualifications and expertise in cybersecurity.
Question: Who is expected to succeed Cairncross?
Kirsten Davies, the current Chief Information Officer at the Pentagon, has been nominated to succeed Sean Cairncross as National Cyber Director, pending Senate confirmation.
Question: What recent incidents prompted concerns regarding U.S. cybersecurity?
Recent technological outages impacting services such as Microsoft and air traffic control have raised concerns about potential vulnerabilities and the need for stronger cybersecurity measures in the U.S.
